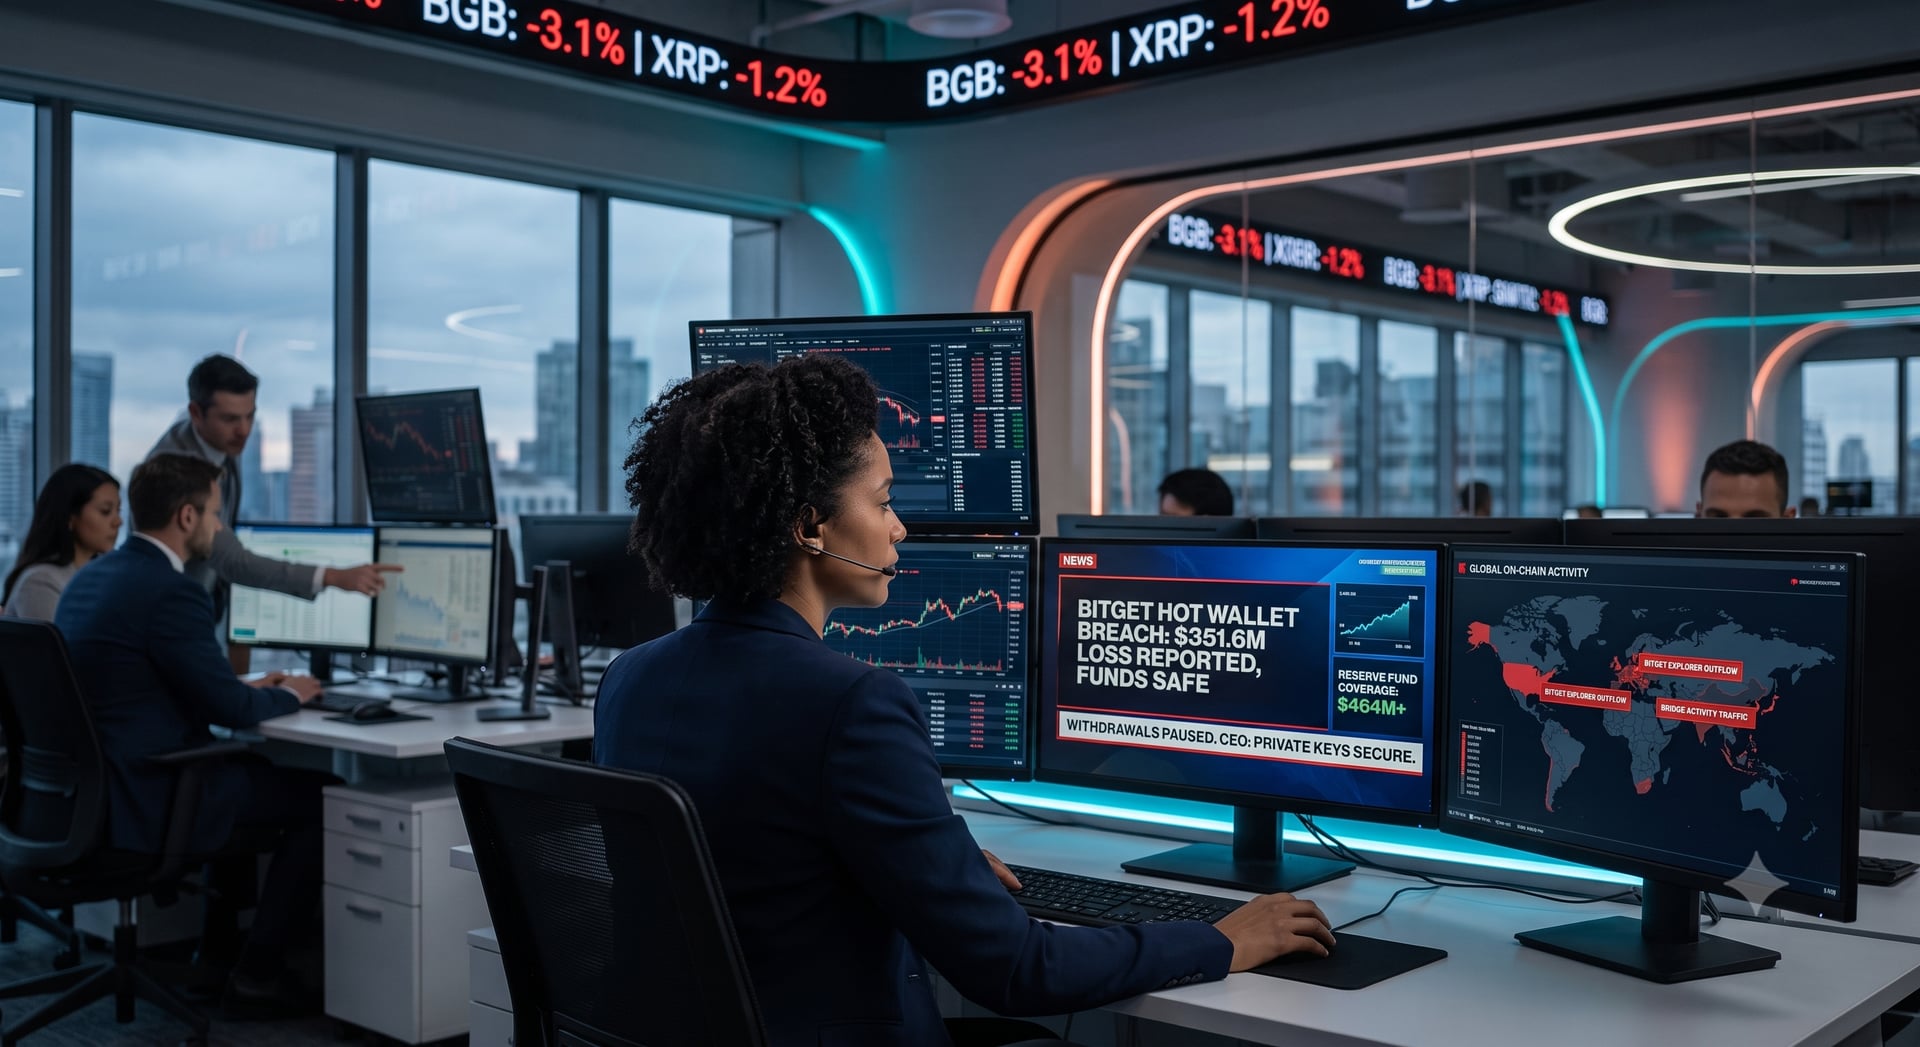
Cryptocurrency exchange Bitget has confirmed an unauthorized outflow of approximately $351.6 million from its hot and warm wallet systems, marking one of the largest security exploits recorded this year.
Bitget leadership acted quickly to reassure the community, confirming that customer account balances remain intact, cold storage was never accessed, and all losses will be fully absorbed by the platform's reserve pool.
What Happened?
At 18:31 UTC on September 24, on-chain intelligence platforms flagged massive, abnormal transfers exiting Bitget hot wallets. The outflows included large tranches of XRP (over 102 million tokens), ETH, USDT, USDC, BNB, and AVAX, which were subsequently routed through decentralized protocols to bridge and swap assets.
Bitget immediately initiated an emergency lockdown, pausing user withdrawals across all networks to isolate the vulnerability.
CEO Gracy Chen Addresses the Incident
In an official public response, Bitget CEO Gracy Chen clarified the attack vector, ruled out key compromises, and confirmed full balance backing:
"A hacker breached one of the core backend systems for our wallet service, used that system to generate false transfer data, and triggered the exchange's authorized approval-signing process to move funds out.
I want to stress that private key compromise has been ruled out... Cold wallets remain fully secure. User funds are safe, and the full amount of this loss falls well within the coverage of Bitget's User Protection Fund, which currently holds over $464 million.
This is absolutely not an FTX scenario. We possess the liquidity and operational capacity to handle concentrated withdrawal requests. Measures to prevent losses from expanding have already been completed, and there is no risk of additional fund outflows."
Key Operational Status
- Wallet Infrastructure: Cold storage remains untouched. Only buffer hot and warm wallets were exposed to the spoofed transaction calls.
- Capital Protection: Bitget's User Protection Fund ($464M+) covers 100% of the affected funds, alongside more than $1 billion in internal company reserves.
- Trading & Deposits: Uninterrupted and operating normally.
- Withdrawals: Temporarily suspended while security teams execute wallet key rotations and complete infrastructure hardening.
- Bitget Wallet (Web3 App): Unaffected; non-custodial decentralized wallets operate on distinct, self-sovereign architecture.
User Safety Advisory
- Watch Out for Phishing: Threat actors actively deploy fake "emergency withdrawal portals" and impersonate customer support during platform freezes. Bitget representatives will never ask for private keys, passwords, or seed phrases.
- No Claim Filing Required: User account balances reflect correct holdings; no manual compensation request is necessary.
- Timeline: The exchange has pledged to release a technical post-mortem and the withdrawal resumption schedule within 24 hours.
This post will be updated as soon as Bitget issues the technical audit report and confirms the reopening schedule for withdrawals.
Discussion (0)
No comments yet. Be the first to join the conversation!